Post-quantum PKI, ready for the 47-day certificate era.
Issue classical, hybrid, and pure post-quantum certificates from one platform. EST and SCEP enrollment, automated short-lived renewal, and non-exportable HSM-backed keys — your stepping stone to PQC migration without a re-platform.
One platform for the whole certificate lifecycle
Keys, certificates, and secrets — classical through post-quantum — with the automation enterprises need as certificate lifetimes collapse.
Hybrid & pure PQC certificates
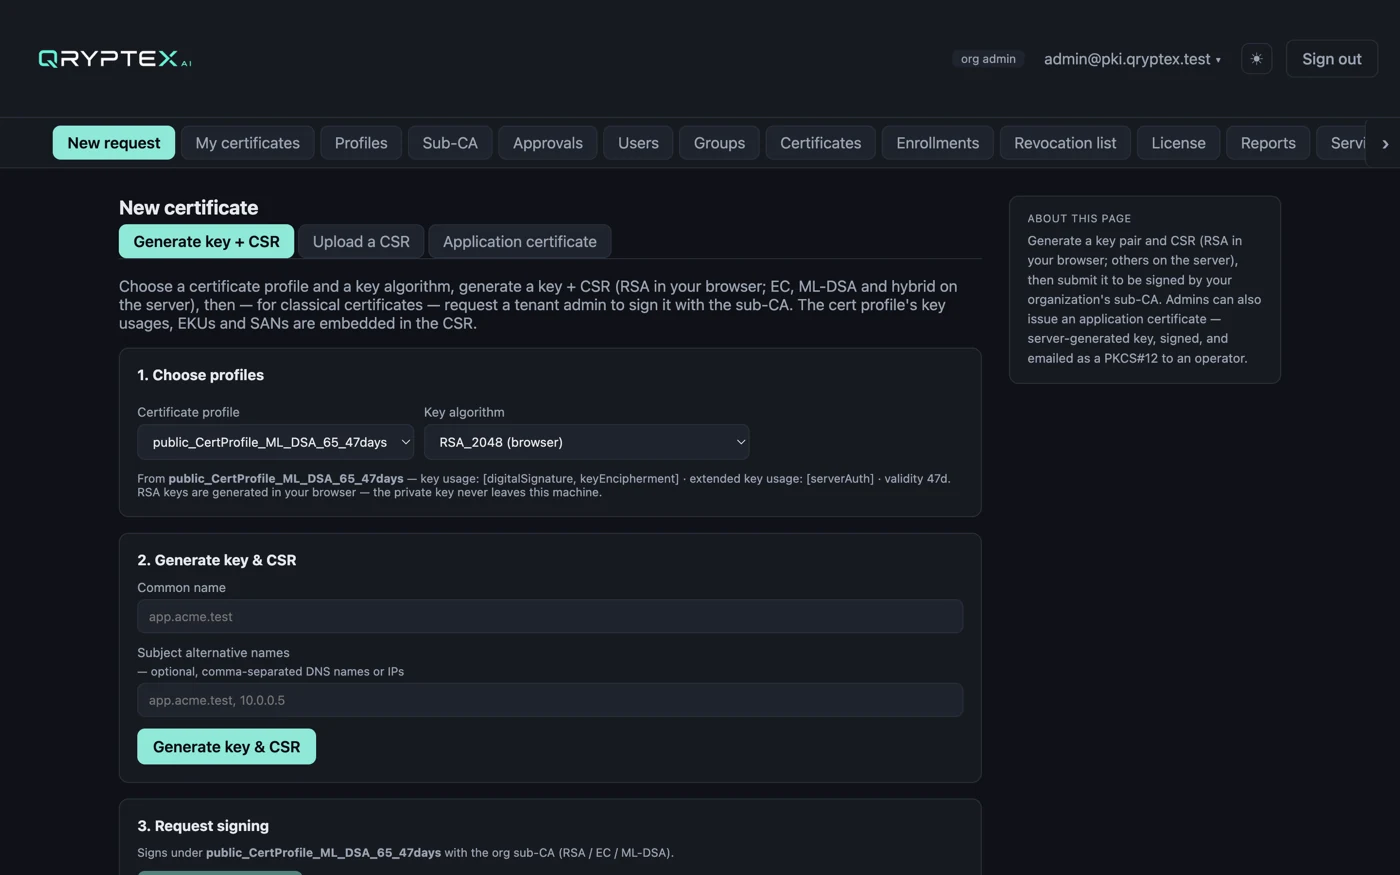
Issue classical, hybrid (classical + PQC), or pure post-quantum certificates from one API. ML-KEM (FIPS 203) and ML-DSA (FIPS 204) alongside RSA, ECDSA and Ed25519.
EST & SCEP, out of the box
Standards-based device enrollment: RFC 7030 EST (simpleenroll / simplereenroll / cacerts / csrattrs) and SCEP for the fleet and network gear you already run.
Automated short-lived certs
Renewal policies with auto-renew keep services live as certificate lifetimes shrink toward 47 days. Automation-first, so short-lived never means more pager duty.
Non-exportable keys, HSM/KMS-backed
CA and tenant keys are generated and used inside the KMS; private keys are never exportable and never touch source, config or logs. Envelope encryption per tenant.
Swap algorithms without re-architecting
Algorithm choice is policy, not plumbing. Move a workload from RSA to hybrid to pure PQC by changing a profile - the issuance, enrollment and renewal paths stay the same.
Isolated tenants from day one
Every request is tenant-scoped from a validated token; row-level isolation in the data tier. Onboard an org in minutes with its own quotas, keys and audit trail.
Audit trail & approvals
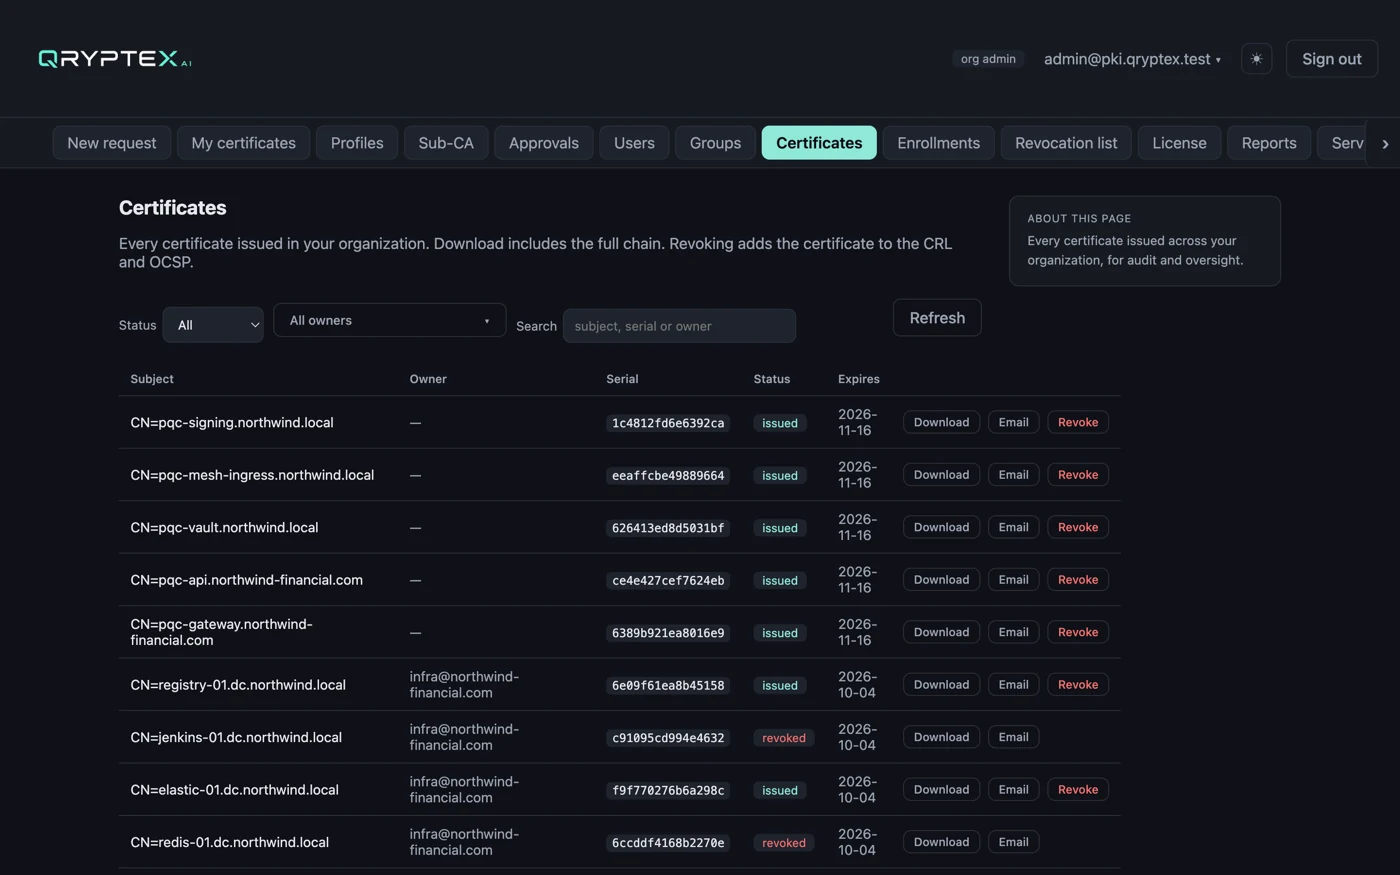
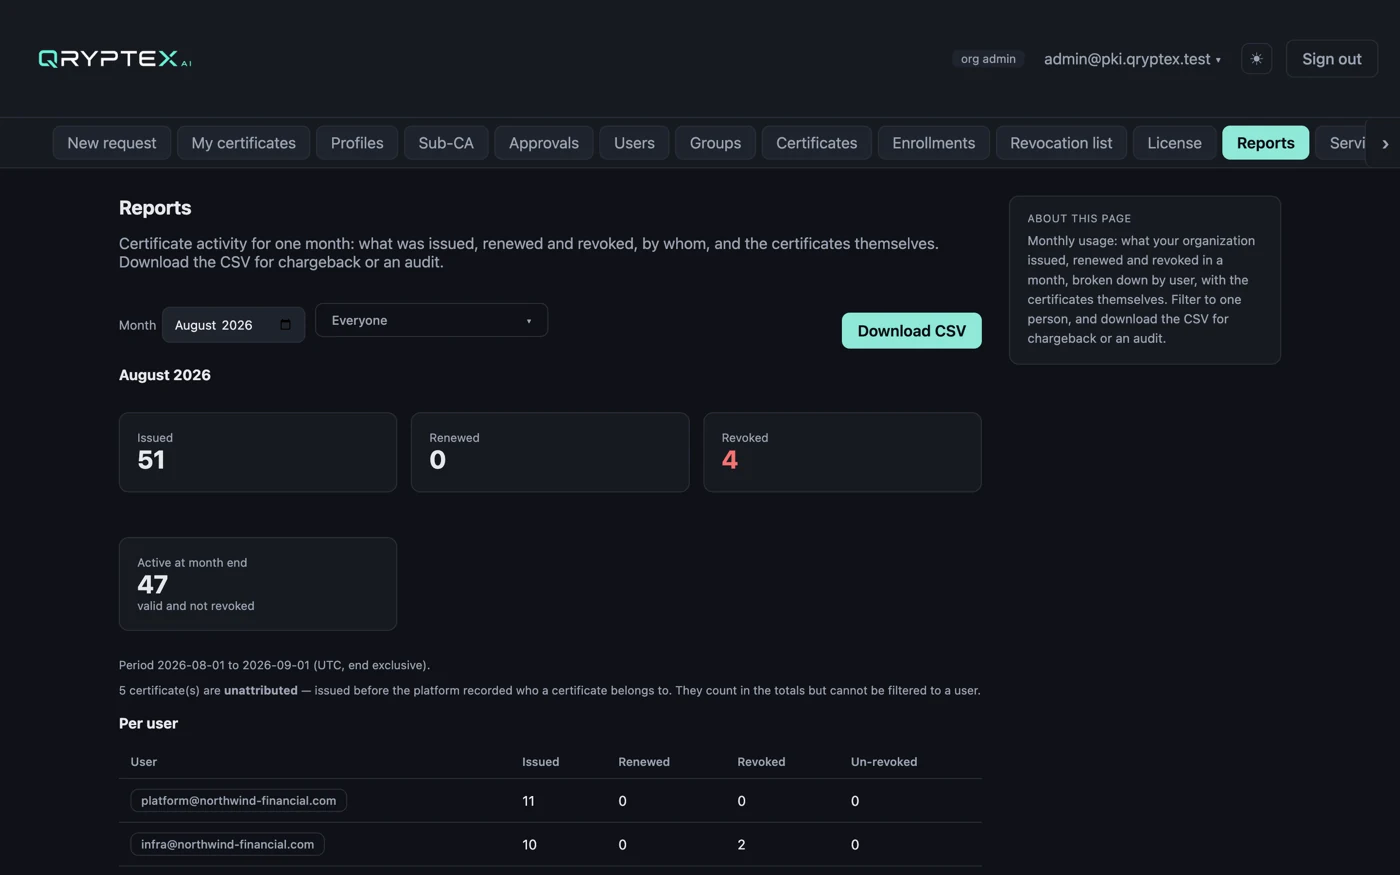
An append-only certificate event log across every issuance channel (portal, EST, SCEP), role-based access control, separation-of-duties approvals, and usage reports built in - not bolted on.
SaaS or self-hosted, same product
Run it as hosted SaaS, or install on your own VM with one command - Docker Compose or Kubernetes. Encrypted, signed backups with local or cloud storage destinations.
Built post-quantum, not patched post-quantum
Real ML-KEM key encapsulation and ML-DSA signatures, issued as hybrid or pure certificates. Pick your posture.
Hybrid (classical + PQC)
A single certificate carries both a classical and a post-quantum signature, so it validates with today's clients while protecting against tomorrow's quantum adversary. The safe default for enterprises mid-migration.
- RSA / ECDSA + ML-DSA
- ECDH + ML-KEM
- Interoperable now
- Harvest-now-decrypt-later resistant
Your stepping stone to PQC migration
Assess & inventory
Discover where classical crypto lives — certificates, keys, devices and endpoints on the network, and the algorithms your code calls directly — then rank by exposure to harvest-now-decrypt-later risk.
Go hybrid
Issue hybrid certificates so workloads stay interoperable with today's clients while gaining post-quantum protection. No big-bang cutover.
Move to pure PQC
As clients catch up, flip profiles to pure ML-DSA / ML-KEM. Crypto-agility means it's a policy change, not a re-platform.
Keep it from coming back
A migrated estate refills if the next release adds more RSA. Scheduled source scans catch quantum-vulnerable cryptography and pre-PQC dependencies as they are written, and file the work as tickets.
Ready for 47-day certificates
The CA/Browser Forum (SC-081) is phasing TLS certificate lifetimes down to 47 days by 2029. Automation-first issuance, EST/SCEP, and renewal policies keep you ahead.
How we compare
| Capability | Qryptex AI | Traditional in-house PKI | Public CA / cloud KMS |
|---|---|---|---|
| Pure PQC (ML-DSA / ML-KEM) | Yes | No | Rare / preview |
| Hybrid (classical + PQC) certs | Yes | No | Rare |
| EST + SCEP enrollment | Yes | DIY | Partial |
| Automated short-lived (47-day) renewal | Yes | Manual | Partial |
| Non-exportable HSM/KMS keys | Yes | If you build it | Yes |
| Crypto-agility (swap algos by policy) | Yes | No | No |
| Multi-tenant isolation | Yes | DIY | Varies |
| Self-host evaluation in minutes | Yes | Weeks | No |
| PQC migration tooling & guidance | Yes | No | No |
Self-host on your own infrastructure
The full platform on your own VM. Request access and we email you a read-only registry login, the install instructions and an evaluation licence — the installer is one command and activation is an upload in the browser.
The images are private, so the install begins with a registry sign-in. Your credentials and the commands arrive with your licence.
Minimum requirements (self-hosted, single VM)
| Minimum | Recommended | |
|---|---|---|
| vCPU | 4 | 8 |
| RAM | 8 GB | 16 GB |
| Disk | 40 GB SSD | 100 GB SSD |
| OS | Linux x86_64 with Docker Engine 24+ | — |
| Network | outbound 443 to our image registry (install and upgrade only) | — |
What you actually get
Screens from a running installation — real certificates issued by its own sub-CA, not mockups.